Tools / Analysis
OpenAI releases GPT-6 Cyber through restricted Daybreak access
The security model is reaching selected approved teams. Its benchmarks and real patch records measure different parts of the work.
OpenAI introduced GPT-6 Cyber on 5 November. Initial access is through the API and Codex for selected, approved Daybreak Red customers, with broader access within that tier planned later.
The system card describes a version of GPT-6 Astra specialised for authorised security work. Its additional training targets both stronger vulnerability research and adherence to the boundaries set by the researcher.
Capability and permission are separate tests
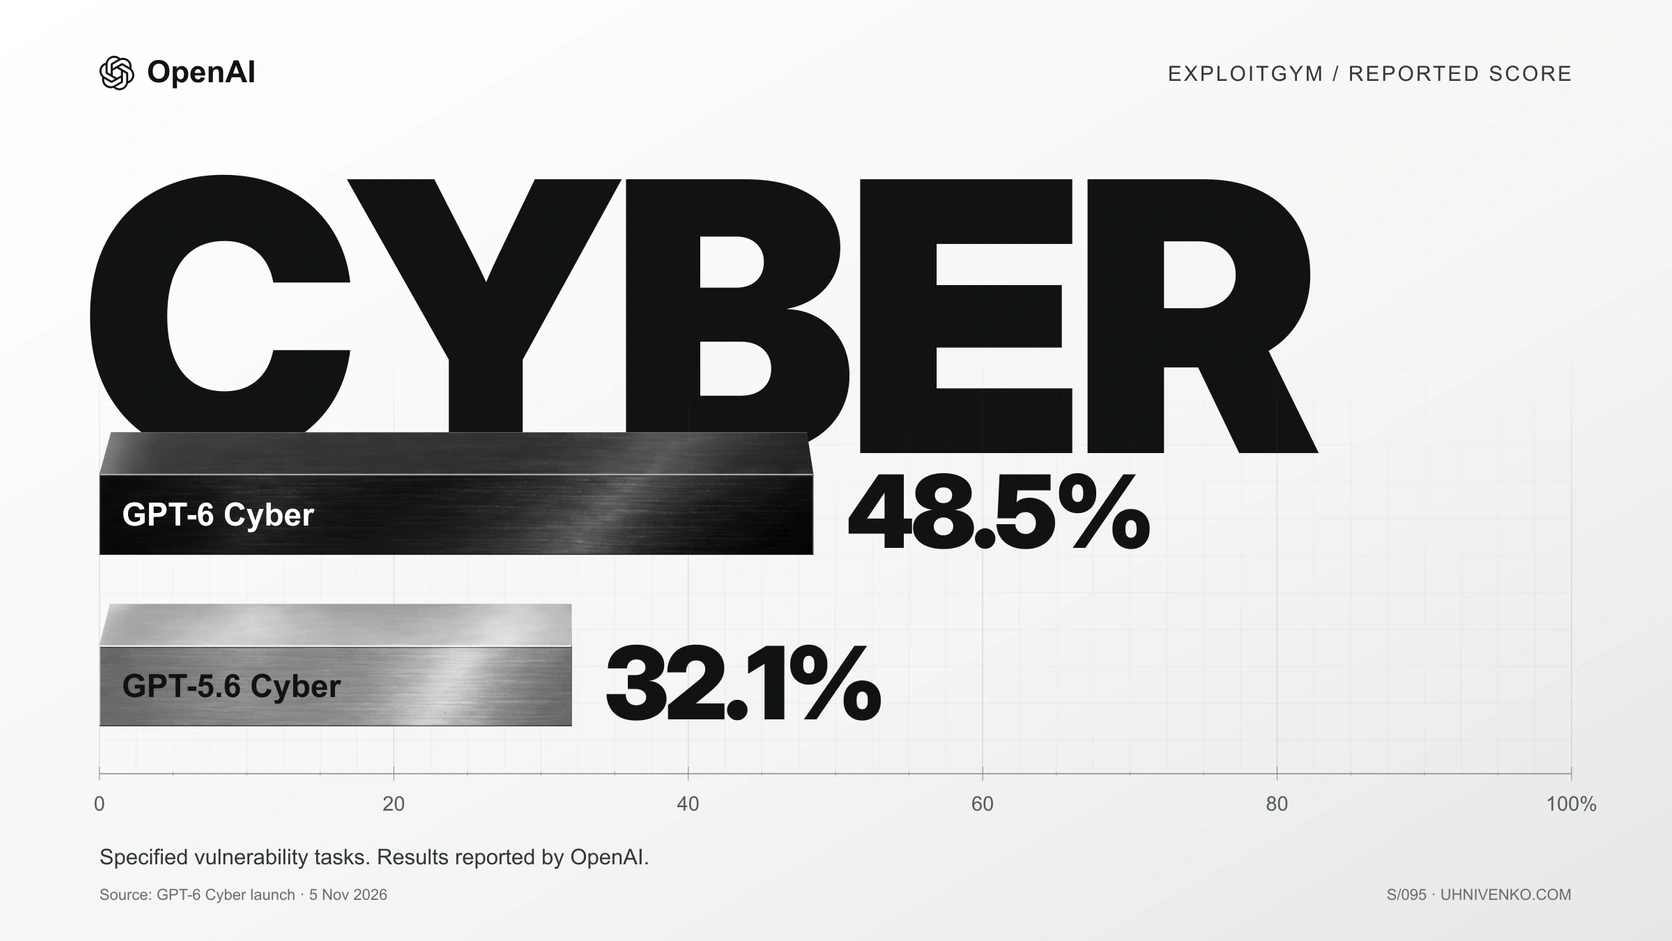
OpenAI reports 48.5% on ExploitGym, compared with 32.1% for GPT-5.6 Cyber. That evaluation gives models specified vulnerabilities to test; it does not measure the proportion of arbitrary software they can compromise.
The system card rates GPT-6 Cyber Critical for cybersecurity under OpenAI’s Preparedness Framework. It also describes separate evaluations of restrictions, honest reporting and unwanted actions. Results are uneven across those checks: stronger security capability should not be read as proof that every autonomous action will remain appropriate.
Sources: OpenAI [1] · OpenAI Deployment Safety Hub [2]
OpenAI’s GPT-6 Cyber announcement
Loading post from X…
Official launch post. Benchmarks are reported by OpenAI.
The evidence has to reach a maintainer
OpenAI’s 4 November Linux study separates the stages of a research pipeline: 2,308 candidate findings, 1,724 reproduced vulnerabilities and 948 working local privilege-escalation exploits. Candidate patches then went through human review before reporting. A suspected bug, a reproducible failure and an accepted fix are distinct outputs; the headline total cannot stand in for all three.
Mozilla supplies a separate, inspectable record of fixes. Its Firefox 159 security advisory, dated 27 October, credits OpenAI researcher Amy Burnett on multiple high-severity entries, including layout, storage and DOM problems. The advisory establishes that those fixes reached a released browser. It does not identify the model used, so attributing their discovery specifically to GPT-6 Cyber still relies on OpenAI’s account.
Sources: OpenAI [3] · Mozilla [4] · OpenAI [1]
Red approval does not automatically unlock the model
The Daybreak documentation says GPT-6 Cyber needs separate model approval. Daybreak Red currently serves approved business and enterprise organisations; the ordinary individual application is for Blue. Access is intended for security work on systems the user owns or is explicitly authorised to test, not resale or downstream customer traffic. For a team considering the model, eligibility and the approved scope are therefore part of deployment planning, alongside the quality of its findings.
Sources: OpenAI Help Center [5]
SOURCES & METHOD
The record behind the article
Based on OpenAI’s release, system card and Linux study, its access documentation, and Mozilla’s advisory. We have not tested the model.
- GPT-6 Cyber: Advancing the frontier of aligned cybersecurity agents OpenAI · 2026-11-05
- GPT-6 Cyber System Card OpenAI Deployment Safety Hub · 2026-11-05
- A thousand fewer paths to root OpenAI · 2026-11-04
- Security Vulnerabilities fixed in Firefox 159 Mozilla · 2026-10-27
- OpenAI Daybreak — Trusted Access for Cyber overview OpenAI Help Center